This product was not featured by Product Hunt yet. It will not be visible on their landing page and won't be ranked (cannot win product of the day regardless of upvotes).
Open-source CLI that tests MCP servers as black boxes. Detects silently changed tool descriptions (rug-pulls), prompt-injection patterns, hidden unicode, schema drift and protocol violations. Runs locally or in CI with JUnit and SARIF reports.
I build AI automation for a living and publish open-source MCP servers, [one of them with 130+ tools]. That's where this came from.
Pin your MCP servers like dependencies. mcpward is an open-source CLI that snapshots an MCP server's contract into a lockfile and fails your build when it changes.
Apache-2.0, runs on Node 22+.
No account, no API key, no telemetry.
[It started because I kept worrying about MCP servers silently changing underneath my agents. I shared it on r/mcp and Hacker News, and the feedback shaped most of what's in it today.]
The problem: Your agent trusts whatever tools/list returns.
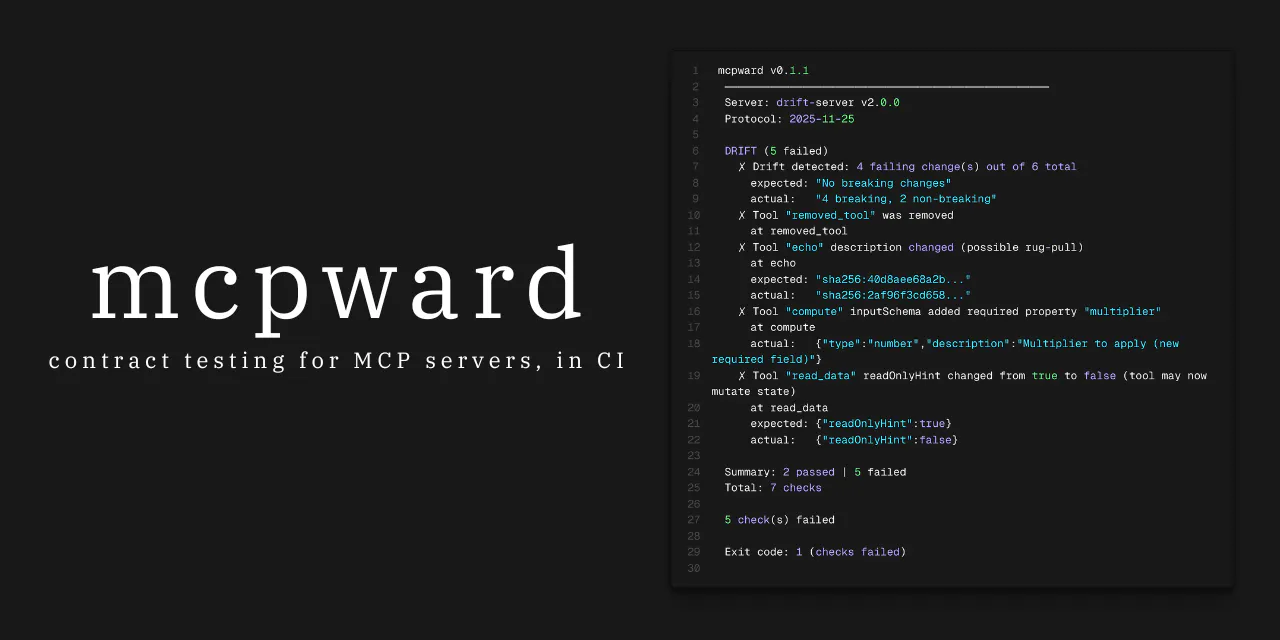
Tool descriptions aren't documentation. They're the instructions the model reads to decide what a tool does. When a server you depend on ships an update, a description can be rewritten, a required parameter can appear, or a read-only tool can start mutating state, and nothing tells you.
mcpward makes those changes fail in CI instead of in production.
What that means in practice:
A rewritten tool description (a "rug-pull") is flagged with a word-level diff, invisible characters included
Every schema change is classified as breaking or non-breaking, so only the ones you care about fail the build
Tool-poisoning checks catch injection phrasing, hidden unicode and schemas that ask for secrets
It's black-box, so it works on servers you didn't write, in any language, over stdio or HTTP
Results go where you already look: JUnit, SARIF for the GitHub Security tab, or a PR comment
Everything runs on your machine. Nothing about your servers is sent anywhere
I read every comment and issue. My favorite check is the hidden-unicode one: add a single zero-width character to a description and watch the diff light up.
No comment highlights available yet. Please check back later!
About mcpward on Product Hunt
“Security & contract testing for MCP servers”
mcpward was submitted on Product Hunt and earned 3 upvotes and 1 comments, placing #96 on the daily leaderboard. Open-source CLI that tests MCP servers as black boxes. Detects silently changed tool descriptions (rug-pulls), prompt-injection patterns, hidden unicode, schema drift and protocol violations. Runs locally or in CI with JUnit and SARIF reports.
mcpward was featured in Open Source (69k followers), Developer Tools (521.5k followers), Artificial Intelligence (481.6k followers) and GitHub (41.4k followers) on Product Hunt. Together, these topics include over 269.5k products, making this a competitive space to launch in.
Who hunted mcpward?
mcpward was hunted by Tsvetan Gerginov. A “hunter” on Product Hunt is the community member who submits a product to the platform — uploading the images, the link, and tagging the makers behind it. Hunters typically write the first comment explaining why a product is worth attention, and their followers are notified the moment they post. Around 79% of featured launches on Product Hunt are self-hunted by their makers, but a well-known hunter still acts as a signal of quality to the rest of the community. See the full all-time top hunters leaderboard to discover who is shaping the Product Hunt ecosystem.
Want to see how mcpward stacked up against nearby launches in real time? Check out the live launch dashboard for upvote speed charts, proximity comparisons, and more analytics.

 Tsvetan Gerginov
Hey @Product Hunt , I'm @tsvetang2 , the maker of mcpward.
I build AI automation for a living and publish open-source MCP servers, [one of them with 130+ tools]. That's where this came from.
Pin your MCP servers like dependencies. mcpward is an open-source CLI that snapshots an MCP server's contract into a lockfile and fails your build when it changes.
Apache-2.0, runs on Node 22+.
No account, no API key, no telemetry.
[It started because I kept worrying about MCP servers silently changing underneath my agents. I shared it on r/mcp and Hacker News, and the feedback shaped most of what's in it today.]
The problem: Your agent trusts whatever tools/list returns.
Tool descriptions aren't documentation. They're the instructions the model reads to decide what a tool does. When a server you depend on ships an update, a description can be rewritten, a required parameter can appear, or a read-only tool can start mutating state, and nothing tells you.
mcpward makes those changes fail in CI instead of in production.
What that means in practice:
A rewritten tool description (a "rug-pull") is flagged with a word-level diff, invisible characters included
Every schema change is classified as breaking or non-breaking, so only the ones you care about fail the build
Tool-poisoning checks catch injection phrasing, hidden unicode and schemas that ask for secrets
It's black-box, so it works on servers you didn't write, in any language, over stdio or HTTP
Results go where you already look: JUnit, SARIF for the GitHub Security tab, or a PR comment
Everything runs on your machine. Nothing about your servers is sent anywhere
It's free and open source.
Try it with
Then run
There's a GitHub Action too: TsvetanG2/mcpward@v1.
I read every comment and issue. My favorite check is the hidden-unicode one: add a single zero-width character to a description and watch the diff light up.