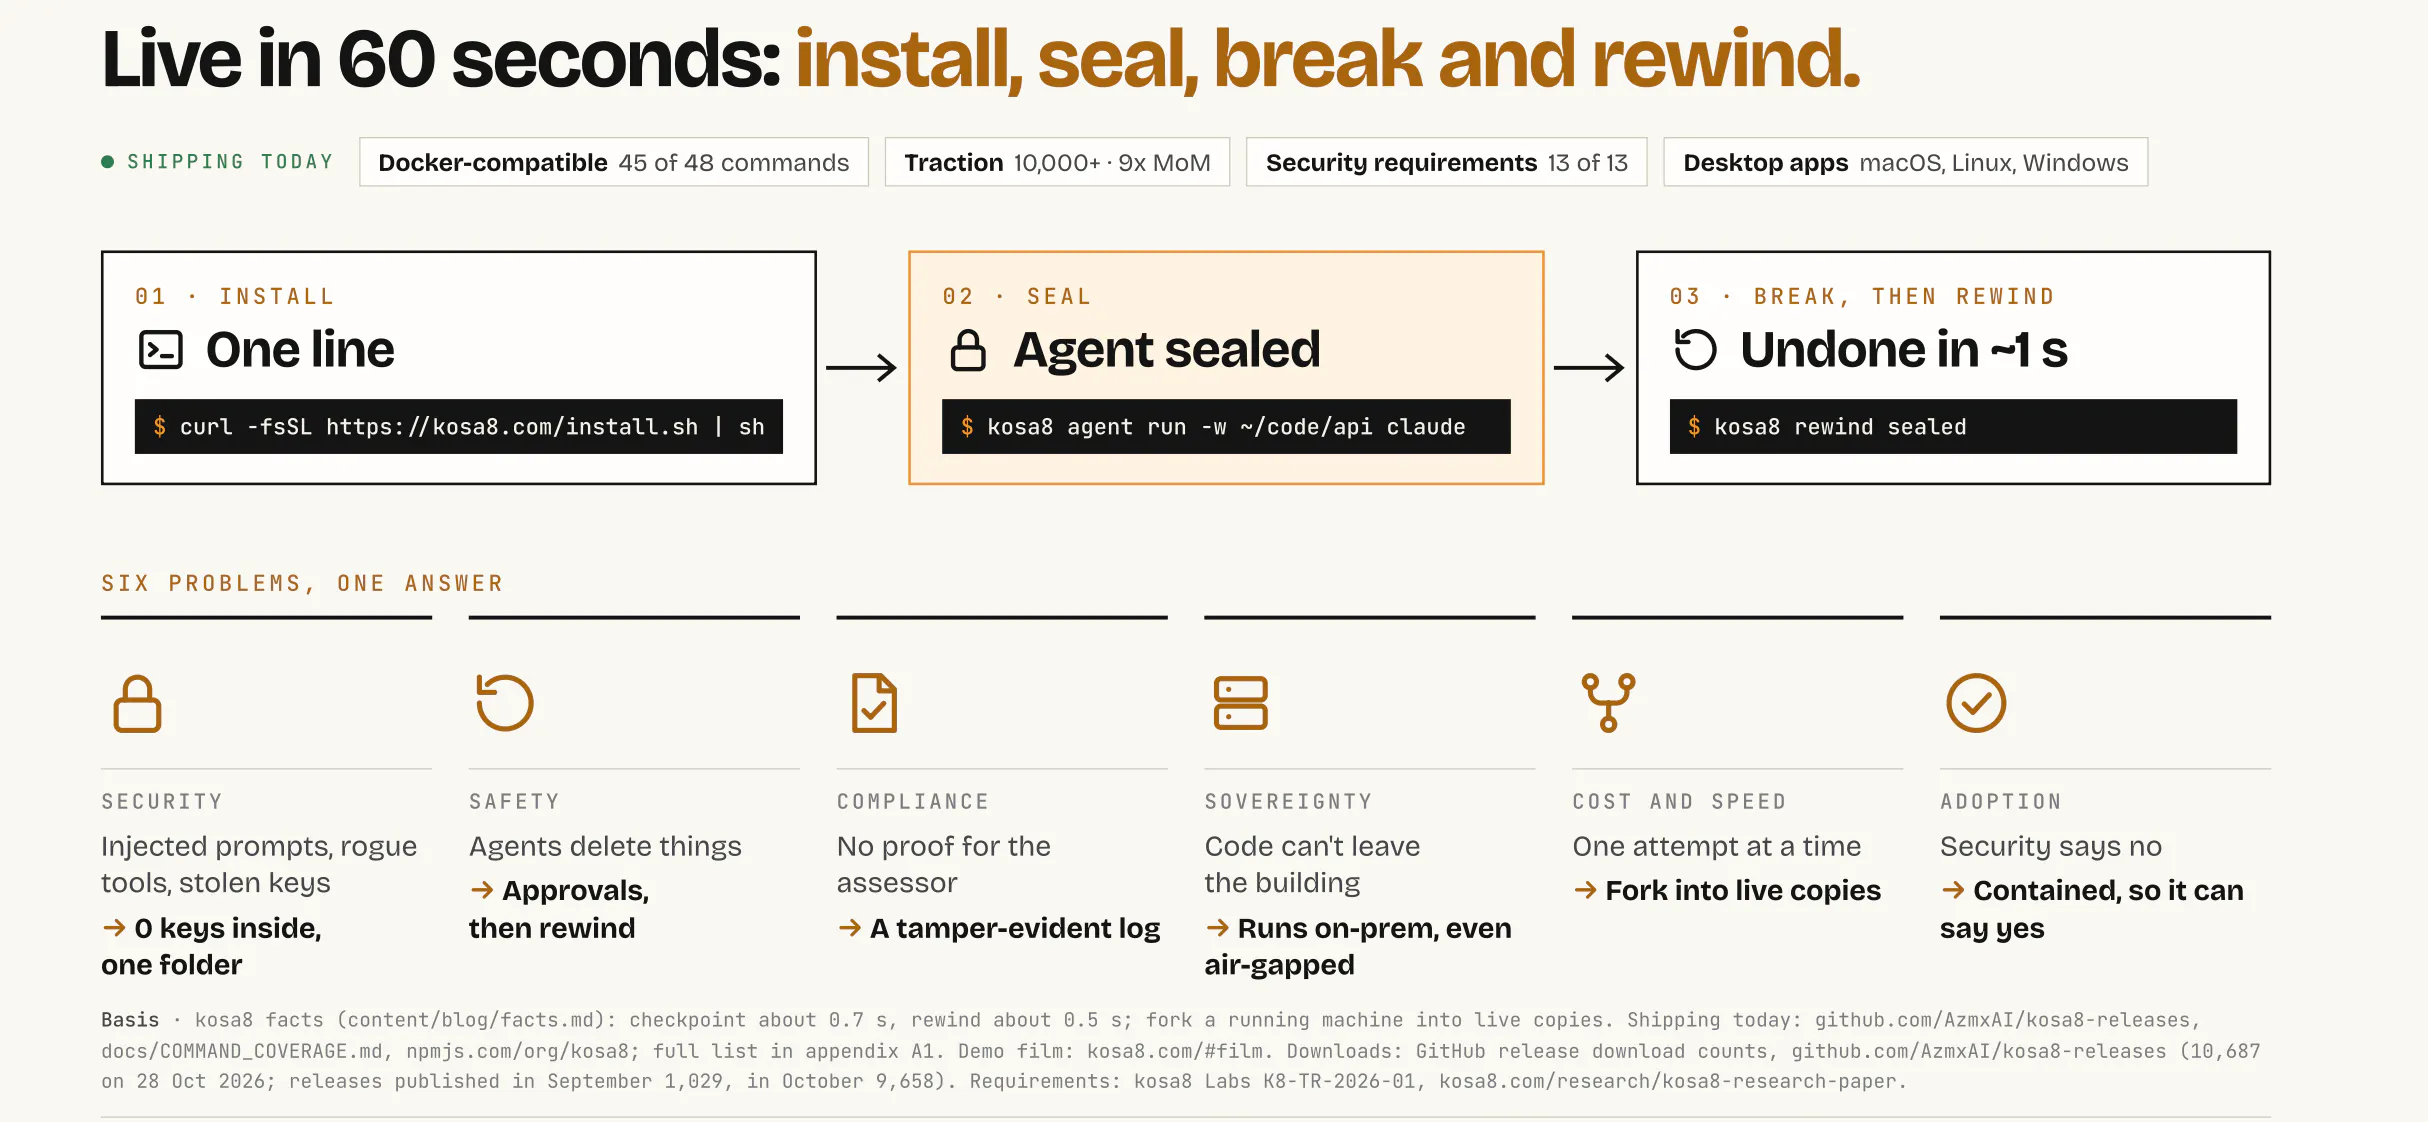
kosa8 is security infrastructure for enterprise internal AI agents. Every agent gets its own microVM with its own kernel, on your Macs, your Linux servers, your cloud, or fully air-gapped. The agent sees one folder, API keys stay on the host (the sandbox holds a placeholder), and the network is closed except the hosts you allow. Rewind the whole machine in about a second when an agent gets it wrong. Docker-compatible, MCP-native, hash-chained audit, signed releases.
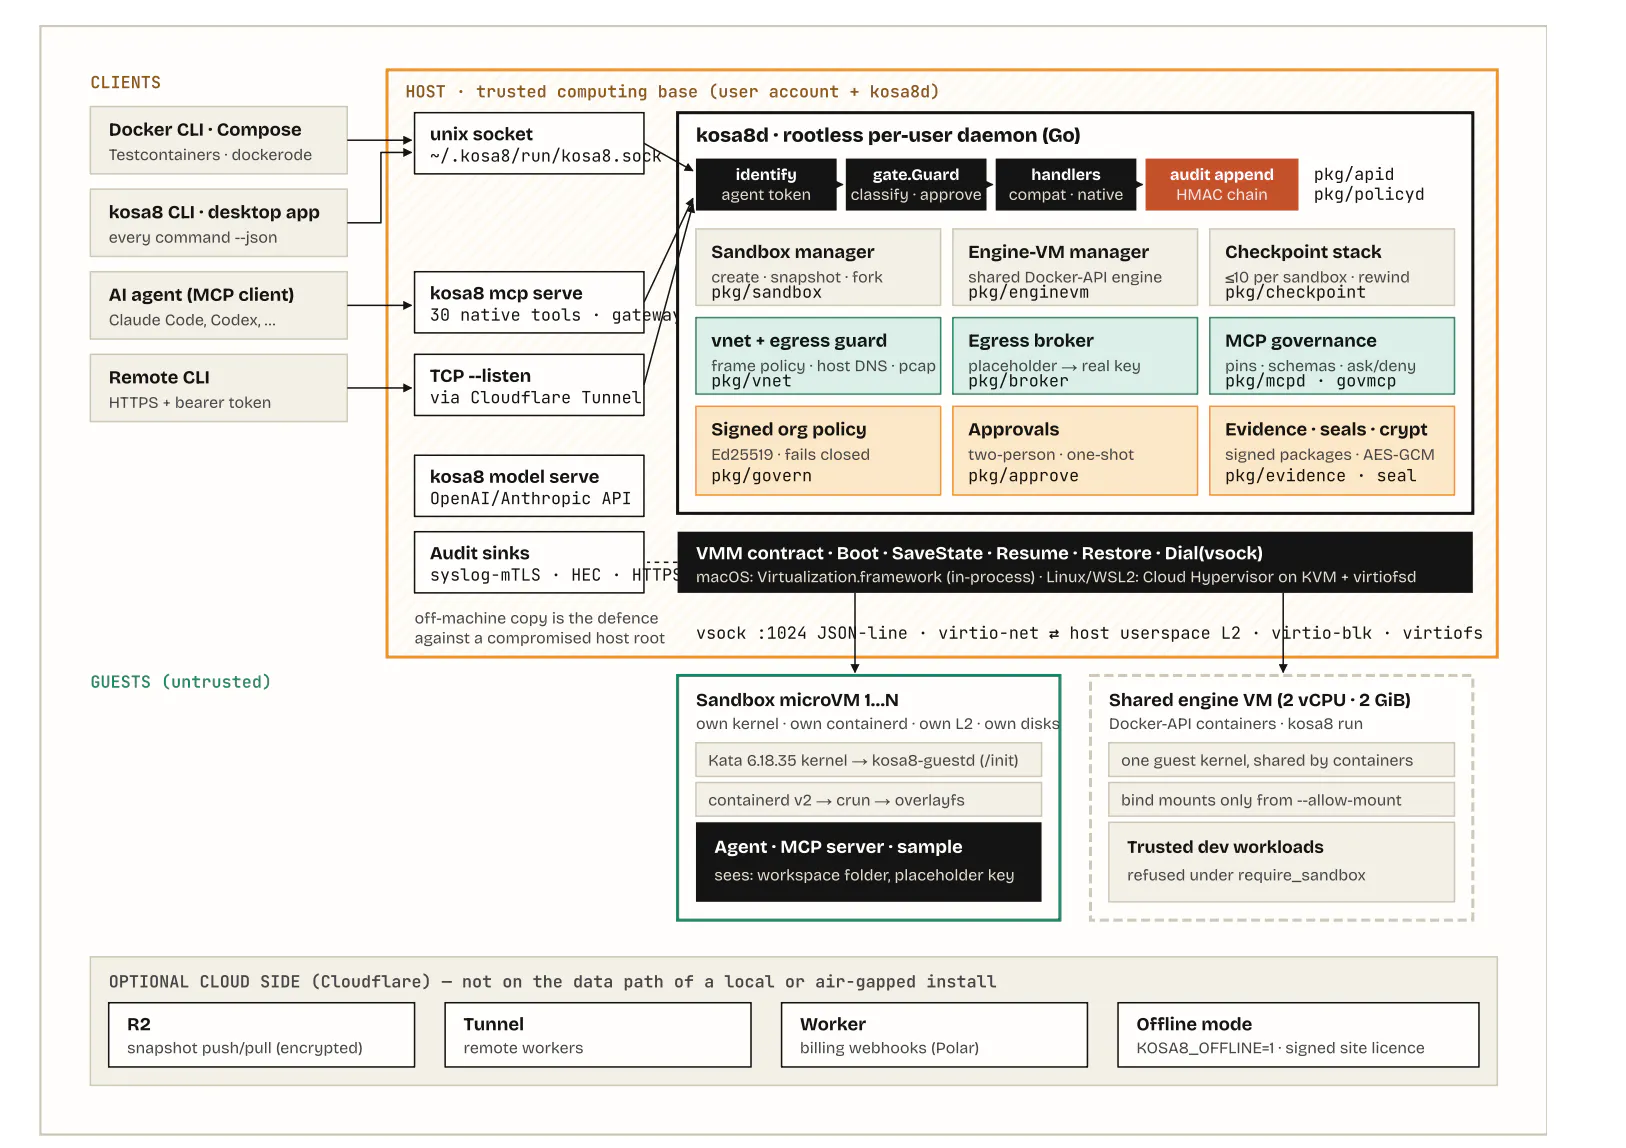
@iamarnob6543 Each sandbox is its own microVM (default 2 vCPU, 1 GiB) with
its own kernel, its own containerd, two virtio-blk disks and an isolated userspace L2 network;
agents, MCP gateway servers, malware detonations and cyber-range trainees always run in
sandboxes. A single shared engine VM (2 vCPU, 2 GiB) serves the Docker-compatible
AP
I for trusted
developer workloads, equivalent to the VM inside Docker Desktop; containers there share one
guest kernel with each other. The signed policy field require_sand
box refuses the engine VM
entirely, which regulated deployments should set.
@kauzovich_anastasiya Enforce outside the guest. Every control that matters runs in the host daemon, so root in the guest cannot disable it. In-guest controls exist only as a second layer.
Local first, cloud optional. The data path never requires a vendor service. Cloud features
(snapshot sync, remote workers) are additive and can be switched off entirely.
Fail closed. A policy that is present but unverifiable stops the daemon; a missing audit key fails
verification; an unclassified API route stops the daemon at start-up.
@grege_rodrigues1 kosa8 is a rootless per-user daemon, kosa8d , plus a command-line client, written in Go (about
90,000 lines of non-test code and 44,500 lines of tests across 62 packages). Figure 4 shows the
components. Clients reach the daemon through a Unix socket (Docker CLI, SDKs, the kosa8 CLI and
desktop apps), through kosa8 mcp serve (A
I agents speaking MCP), or through a token-guarded
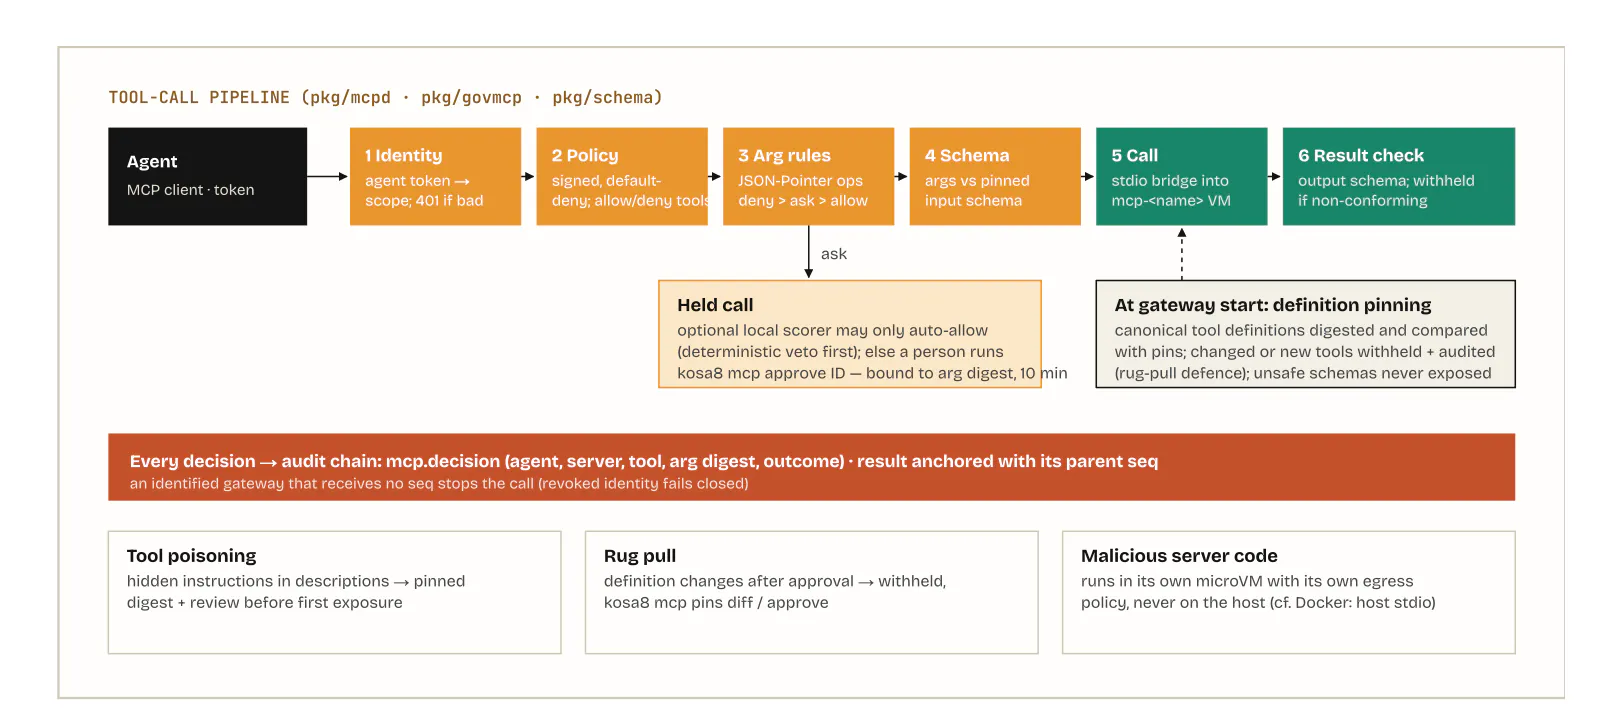
TCP listener (remote CLIs). Every request passes the same pipeline: identify the caller (verifying an
agent token if presented), gate it (classify the route and enforce approvals), run the handler, and
append an audit entry. The gate panics at start-up if any route is unclassified, so a new endpoint
cannot ship ungoverned.
The checkpoint and rewind feature sounds especially useful. Excited to see where kosa8 goes!
@yang_zhang21kosa8 can def. provide Wanaka Studio a safer agentic experience to develop..support each other
Keeping API keys outside the sandbox makes a lot of sense. Congrats, team!
when you fork a brokered sandbox does the fork get its own placeholder and broker
@busmark_w_nika@dipanjan_dey@srikrishna_swaminathan AI agents are moving into real work: running code, touching files, calling APIs. But in regulated industries, one question blocks almost every rollout: "How do we prove the agent stayed in its lane?"
We built kosa8 to answer that with infrastructure, not prompts. Every agent gets its own sealed microVM, real keys stay outside, and every action is recorded.
What it means for each sector:
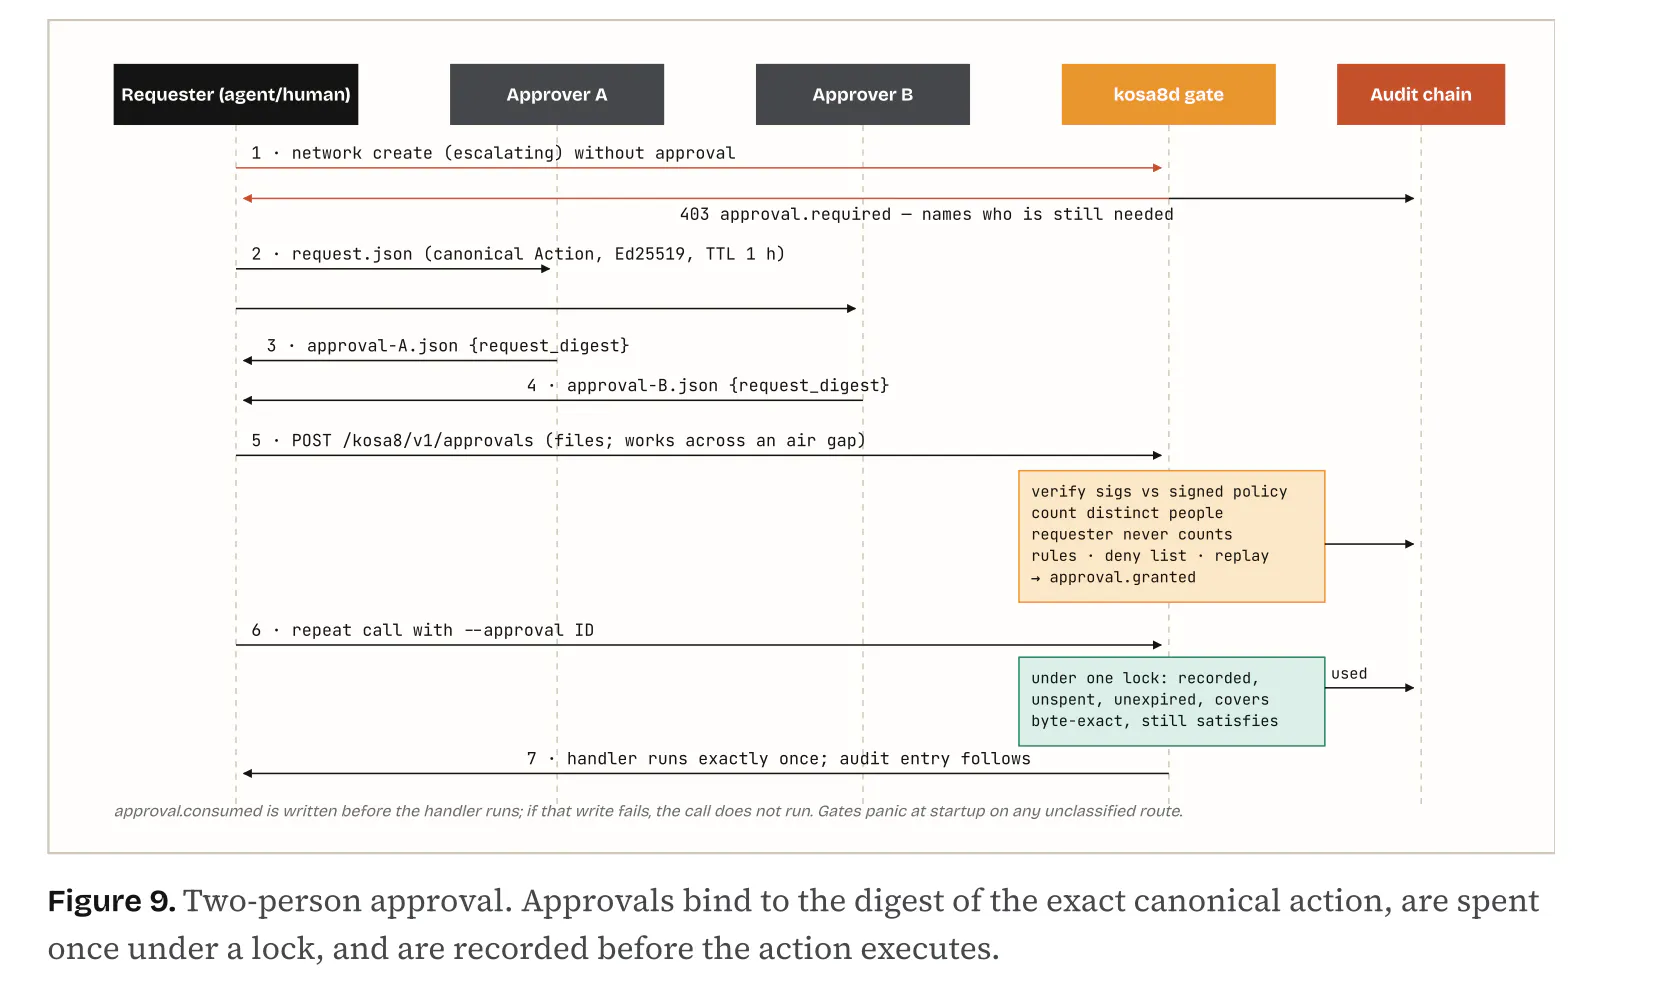
Finance: data stays in the bank, no real keys inside agents, two-person approval for payments and changes, and an audit-ready log for regulators.
Healthcare: patient data never leaves, local AI models, agents see only the records they need, and every action is recorded.
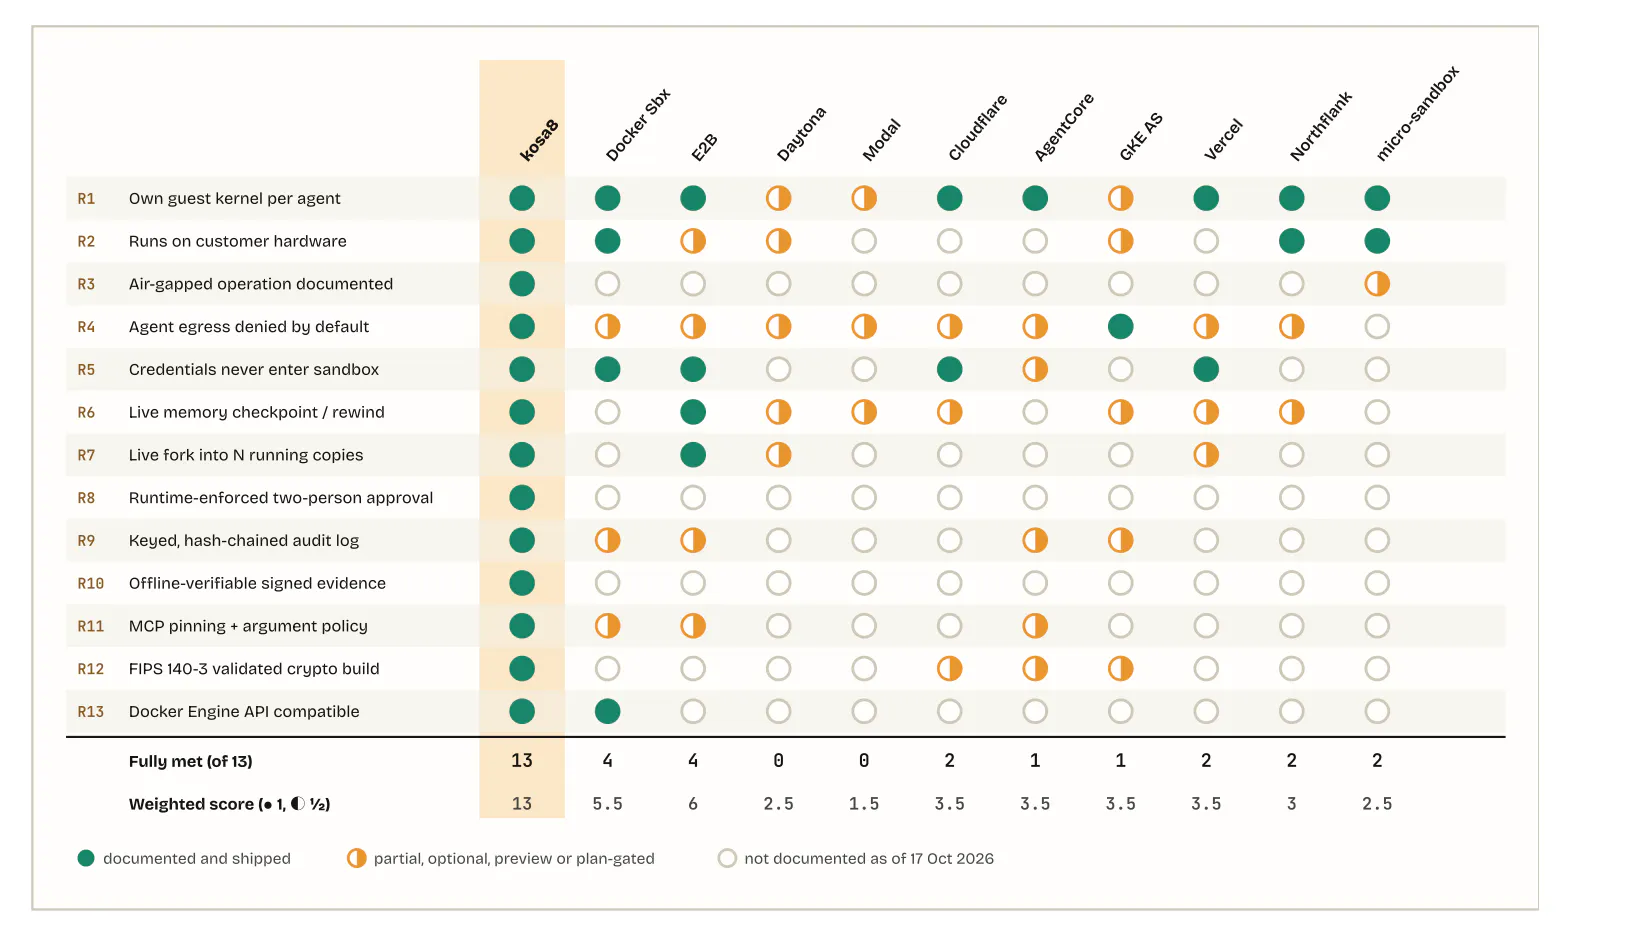
Government: fully air-gapped, FIPS 140-3 builds, the two-person rule, and signed releases you can verify.
The idea is simple: let agents do sensitive work, with security built in and proof ready for auditors.
Curious to hear from people in these industries:
👉 What's the #1 thing stopping your team from letting AI agents touch sensitive data today?
@hamza_afzal_buttBuilding a zero‑trust pipeline with sealed microVMs
When you combine sealed microVMs, an egress broker, and an immutable audit trail, you create a zero‑trust environment for AI agents. The agent never holds secrets, cannot reach the internet except through approved hosts, and any deviation is captured for forensic review.
If you need to test alternative approaches, fork the running machine into live copies—up to eight at once—so you can experiment in parallel without contaminating the original state. Once the winning variant is identified, delete the failed forks and keep the clean checkpoint.
@ravibits congtas on ur AgentKit ..kosa8 making sure safest of Agents ...Agentkit
@thisiskp_ AI agents now act on their own, but regulated teams can't let them run without containment and proof. kosa8 gives them both: - Sealed: every agent gets its own microVM and sees only one folder.
- No secrets inside: real keys stay on the host, and the network only reaches sites you allow.
- Safe tools: MCP servers plug in unchanged, each sealed, with allow/deny/ask rules.
- Undo and branch: rewind a running machine in about half a second, or fork it into 100 live copies in 2.5 seconds.
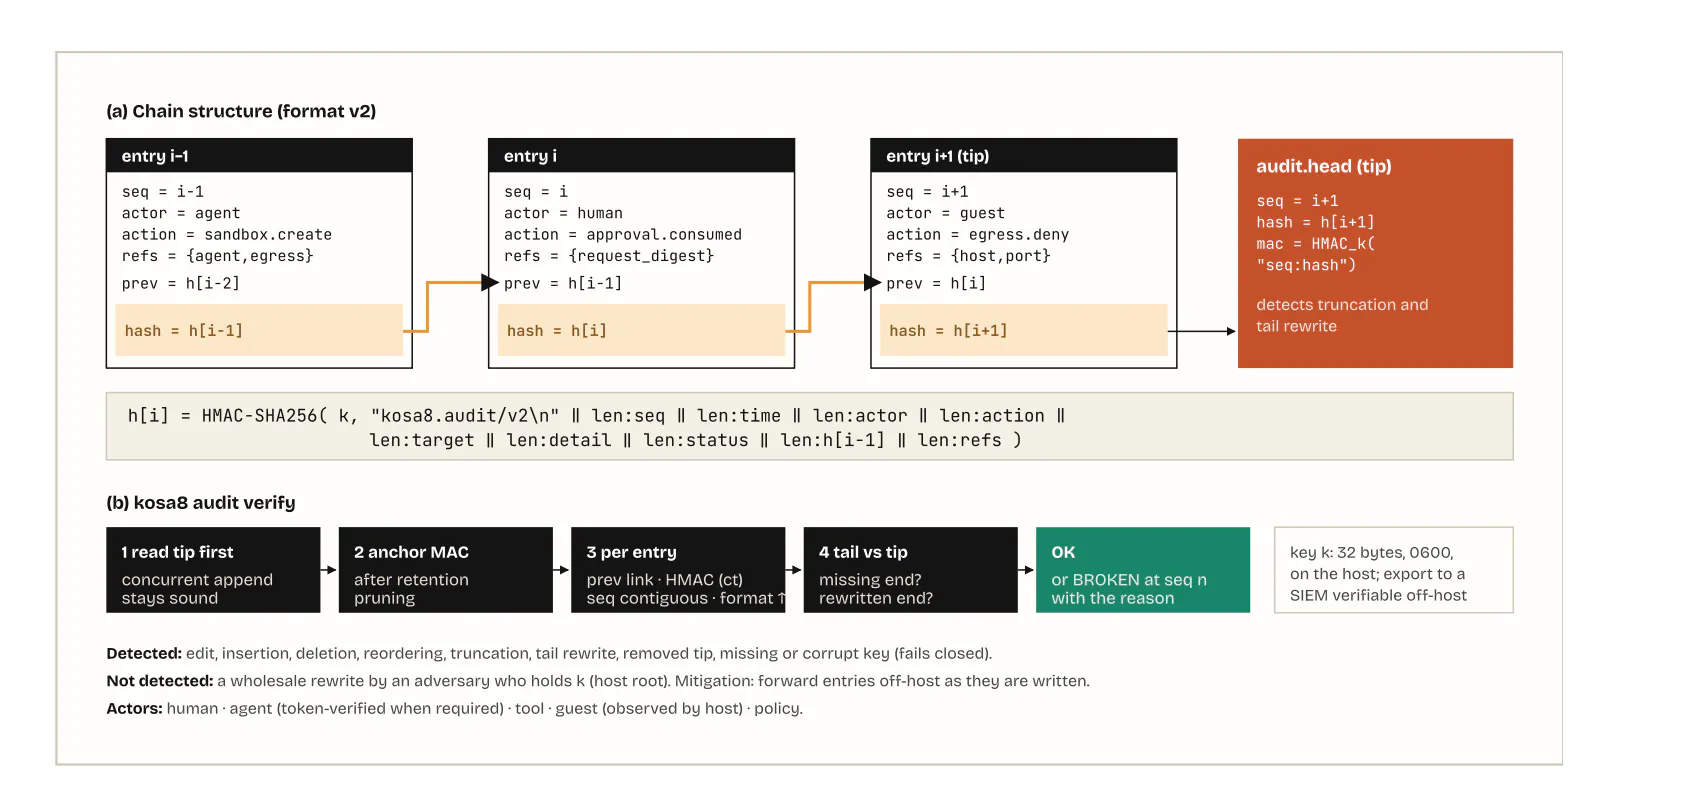
- Proof: a tamper-evident audit log, plus FIPS 140-3 builds.
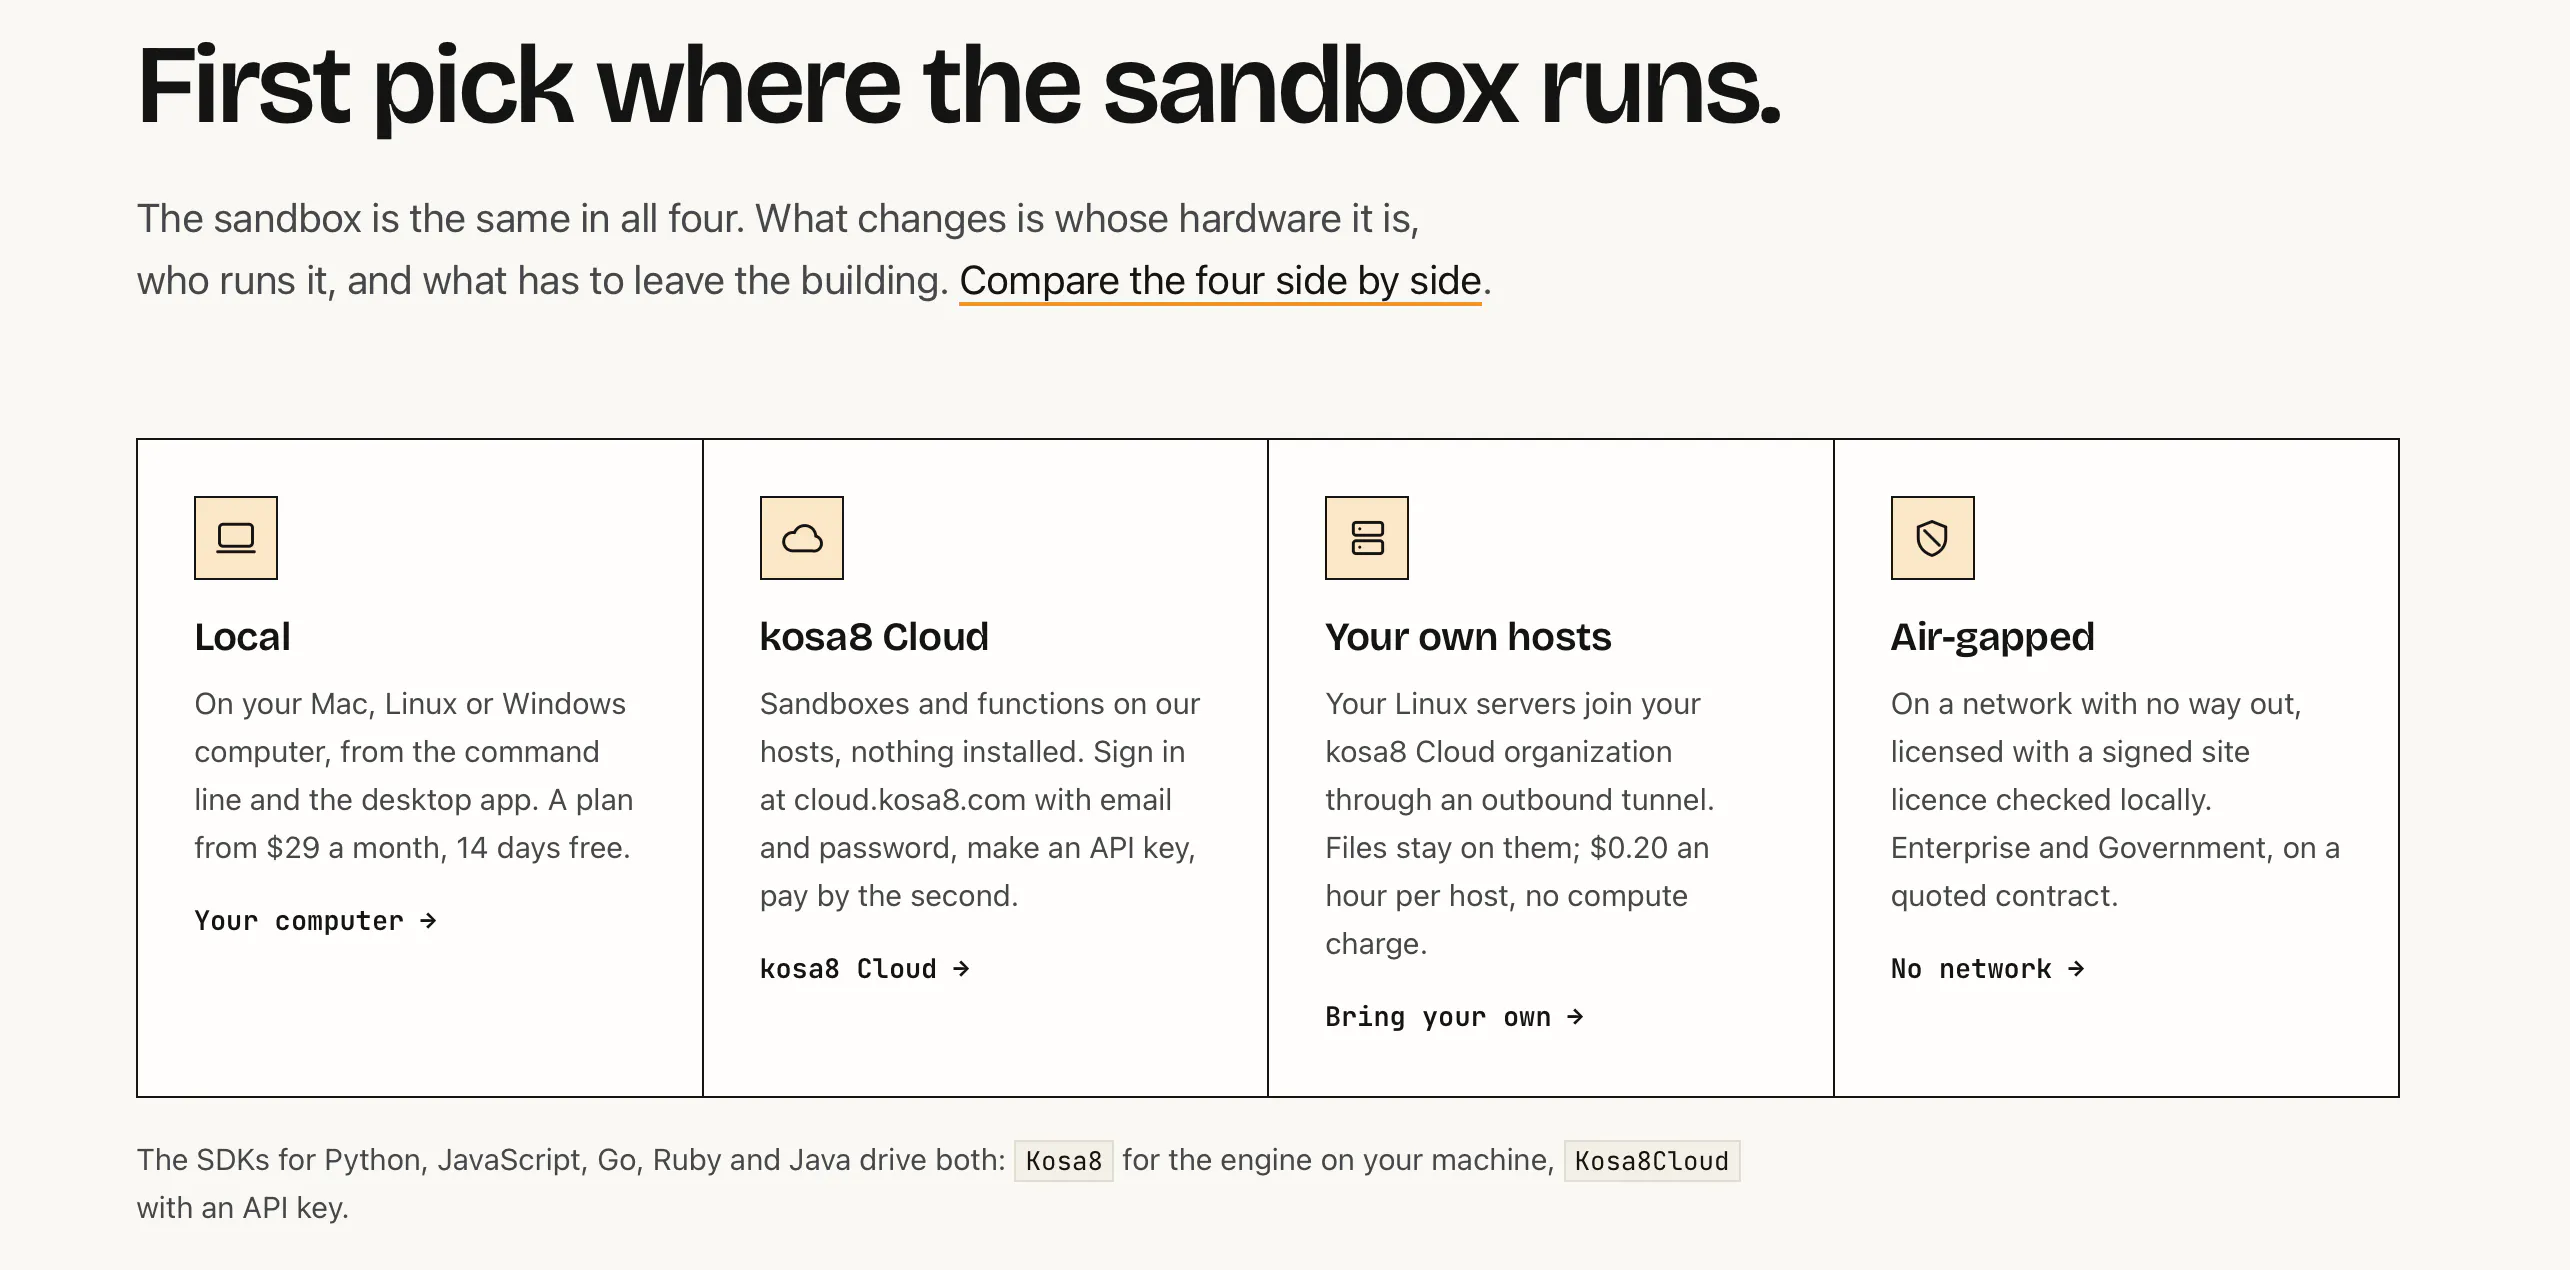
- Runs anywhere: on your laptop, on-prem, air-gapped or on your own cloud servers (BYOC), with kosa8 Cloud coming soon.
- Fits your stack: Docker-compatible, with SDKs in Python, TypeScript, Go, Ruby and Java.
@chrismessinaSovereignty: air gap, FIPS and supply chain for AI Agents :An air-gap bundle contains the binaries, guest kernel, root filesystem and base image with an
installer that fetches nothing; KOSA
8_OFFLIN
E=1 refuses all outbound calls; a site licence is an
Ed25519-signed file verified locally with no activation or phone-home. A FI
PS build compiles
against Go's CMVP
-validated cryptographic module ( GOFIPS140=certified ), and the signed policy
can require it, in which case the daemon refuses to start otherwise; every primitive kosa8 uses
(SHA-256, HMAC-SHA256, Ed25519, AES-GCM, ECDSA, the DRBG) comes from that module.
“Air-gapped microVM sandboxes for enterprise AI agents”
kosa8 launched on Product Hunt on November 4th, 2026 and earned 151 upvotes and 35 comments, placing #5 on the daily leaderboard. kosa8 is security infrastructure for enterprise internal AI agents. Every agent gets its own microVM with its own kernel, on your Macs, your Linux servers, your cloud, or fully air-gapped. The agent sees one folder, API keys stay on the host (the sandbox holds a placeholder), and the network is closed except the hosts you allow. Rewind the whole machine in about a second when an agent gets it wrong. Docker-compatible, MCP-native, hash-chained audit, signed releases.
kosa8 was featured in Developer Tools (522.4k followers), Artificial Intelligence (482.8k followers) and Security (3k followers) on Product Hunt. Together, these topics include over 233.3k products, making this a competitive space to launch in.
Who hunted kosa8?
kosa8 was hunted by fmerian. A “hunter” on Product Hunt is the community member who submits a product to the platform — uploading the images, the link, and tagging the makers behind it. Hunters typically write the first comment explaining why a product is worth attention, and their followers are notified the moment they post. Around 79% of featured launches on Product Hunt are self-hunted by their makers, but a well-known hunter still acts as a signal of quality to the rest of the community. See the full all-time top hunters leaderboard to discover who is shaping the Product Hunt ecosystem.
Want to see how kosa8 stacked up against nearby launches in real time? Check out the live launch dashboard for upvote speed charts, proximity comparisons, and more analytics.

 fmerian
@bsy0221 @kevin @c_randieri @Q by SubStrata @quentindty @chrismessina @varrr_al @X